Adversary Emulation · Strategic Partner
SCYTHE
Adversarial Exposure Validation platform to prove your defenses work, before attackers do.
Visit official website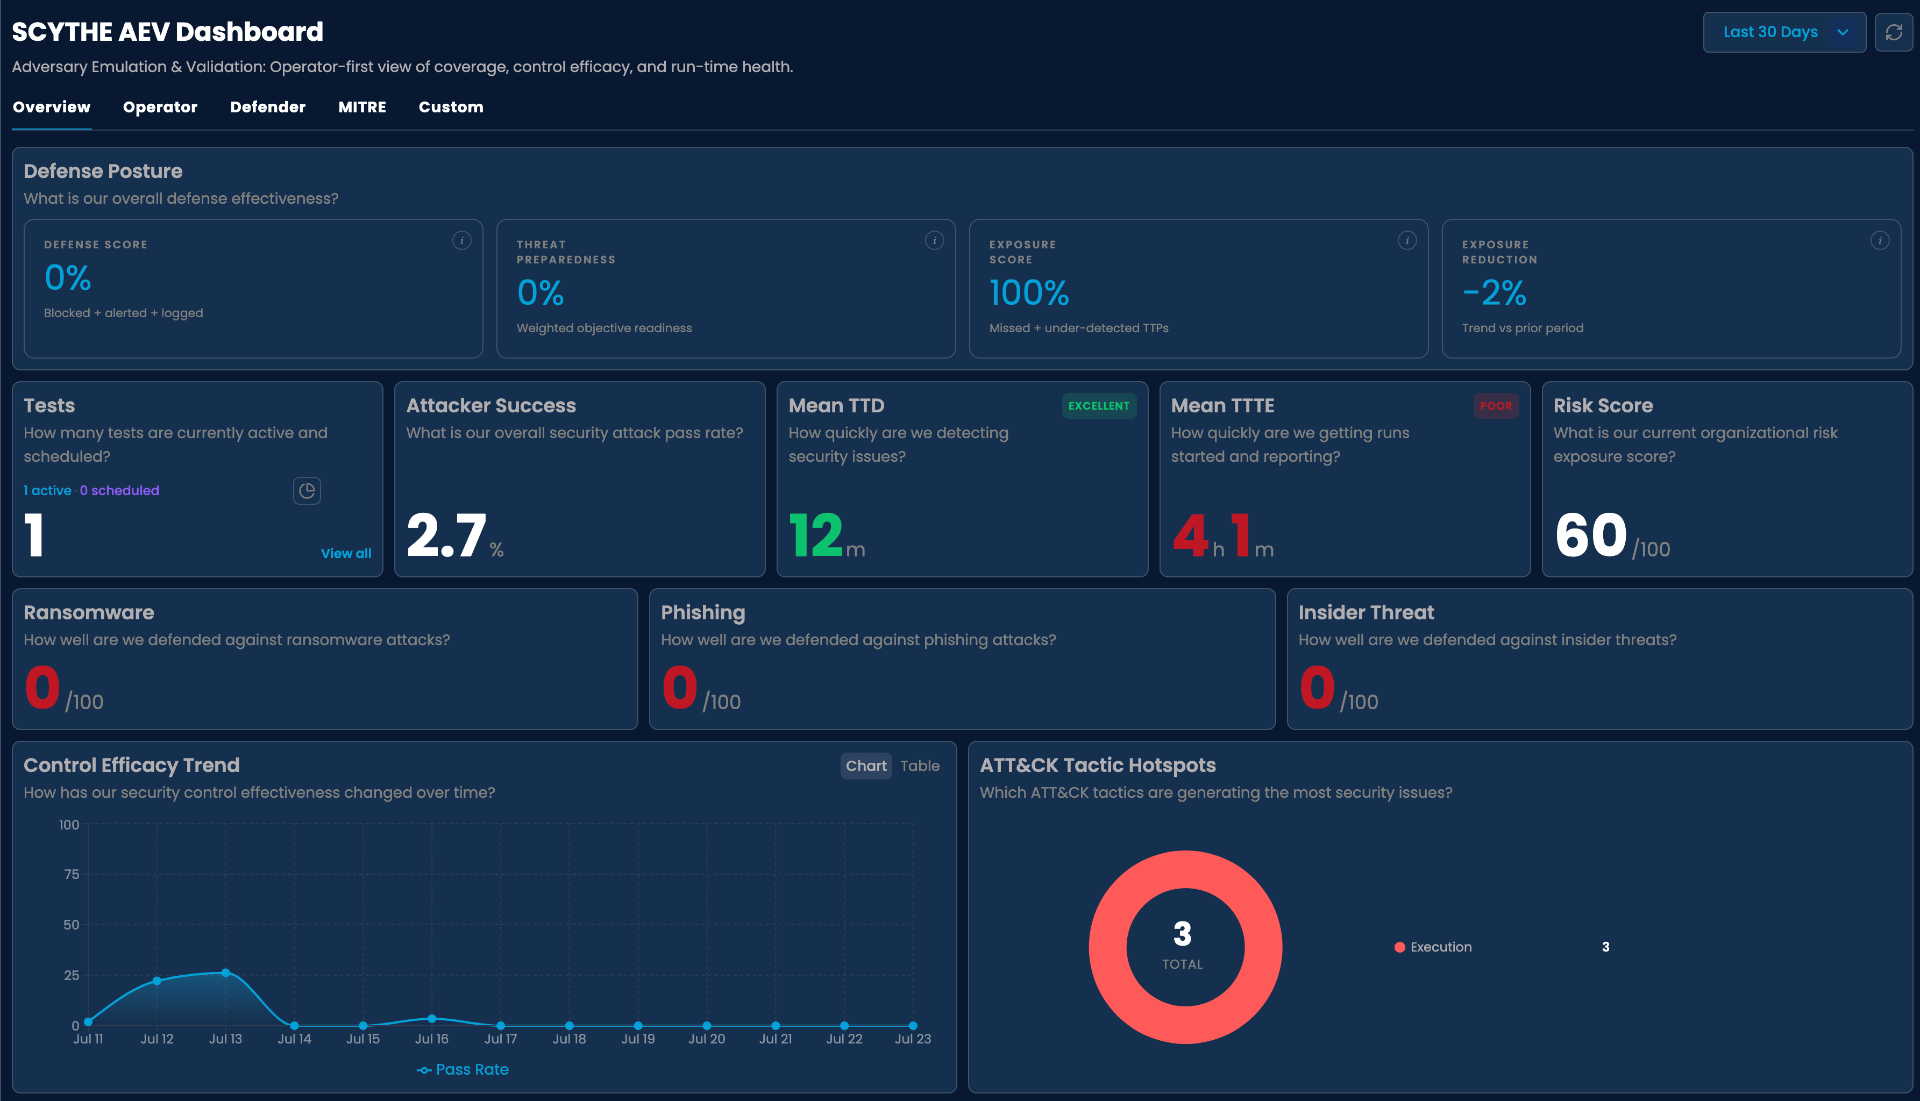
About the partnership
SCYTHE is an Adversarial Exposure Validation platform that runs real MITRE ATT&CK-mapped campaigns in your actual environment on a continuous schedule, validating detection, alerting, and response against the threat actors targeting your industry right now. CROSS-INTEL partners with SCYTHE to deliver continuous adversary emulation and security control validation across IT, cloud, and OT environments in Europe, LATAM, Brazil, the United States, and the Middle East.
Capabilities
Pen Testing, BAS, and AEV · what is the difference
Pen testing is a point-in-time assessment. BAS (Breach and Attack Simulation) automates known attack scenarios. AEV (Adversarial Exposure Validation) goes further: it continuously emulates real adversaries end-to-end in production-like conditions, so you validate not only if a control fires, but whether the full detection, alerting, and response chain actually works against the threats targeting you today.
- Pen Testing · human-led, deep, periodic, narrow scope.
- BAS · automated, broad coverage of atomic techniques, limited context.
- AEV · continuous, threat-informed, full-chain emulation with measurable outcomes.
Operational CTI & SOC Validation
Turn threat intelligence into executable emulation plans. Validate Sigma rules, EDR content, and custom SOC playbooks against the exact TTPs used by the adversaries in your CTI feed, and measure whether your team detects, triages, and responds within the expected window.
- Convert CTI reports into MITRE ATT&CK-mapped emulation campaigns.
- Test Sigma rules and detection content in the real environment.
- Validate custom SOC playbooks and IR runbooks end-to-end.
OT & ICS Security Validation
Emulate adversary behavior safely against OT and ICS environments to validate segmentation, monitoring, and response for industrial operations. Purpose-built to respect the operational constraints of critical infrastructure.
- Threat-informed emulation aligned to ICS-specific TTPs.
- Validate IT/OT segmentation and east-west detection.
- Exercise IR playbooks for critical infrastructure incidents.
Why CROSS-INTEL × SCYTHE
- Joint go-to-market across Europe, LATAM, Brazil, the United States, and the Middle East.
- CROSS-INTEL provides regional sales, adversary emulation engineering, and managed validation operations.
- Continuous validation of EDR, SIEM, SOC and IR playbooks against real threat actor TTPs.
- Alignment with MITRE ATT&CK, NIST CSF, ISO 27001 and sector-specific frameworks.
Joint offering
What we deliver
- →Continuous adversary emulation aligned to MITRE ATT&CK
- →Detection engineering and SOC control validation
- →Threat-informed campaigns for IT, cloud, and OT environments
- →Purple team exercises and detection gap remediation
- →Managed adversarial exposure validation as a service
Industries
Regions
Europe · LATAM · Brazil · United States · Middle East
Certifications & status
Talk to a CROSS-INTEL × SCYTHE specialist
Request a tailored briefing, proof-of-value, or commercial proposal.
Request a consultation