The Pyris Product Family
CROSS-INTEL · The Pyris Platform
The Pyris product family
Six products, one brand family, built on shared foundations: the same threat knowledge, a strict egress gate, and a receipt for every claim. Together they cover the full arc, from knowing what is exposed to proving it, detecting it, and responding.
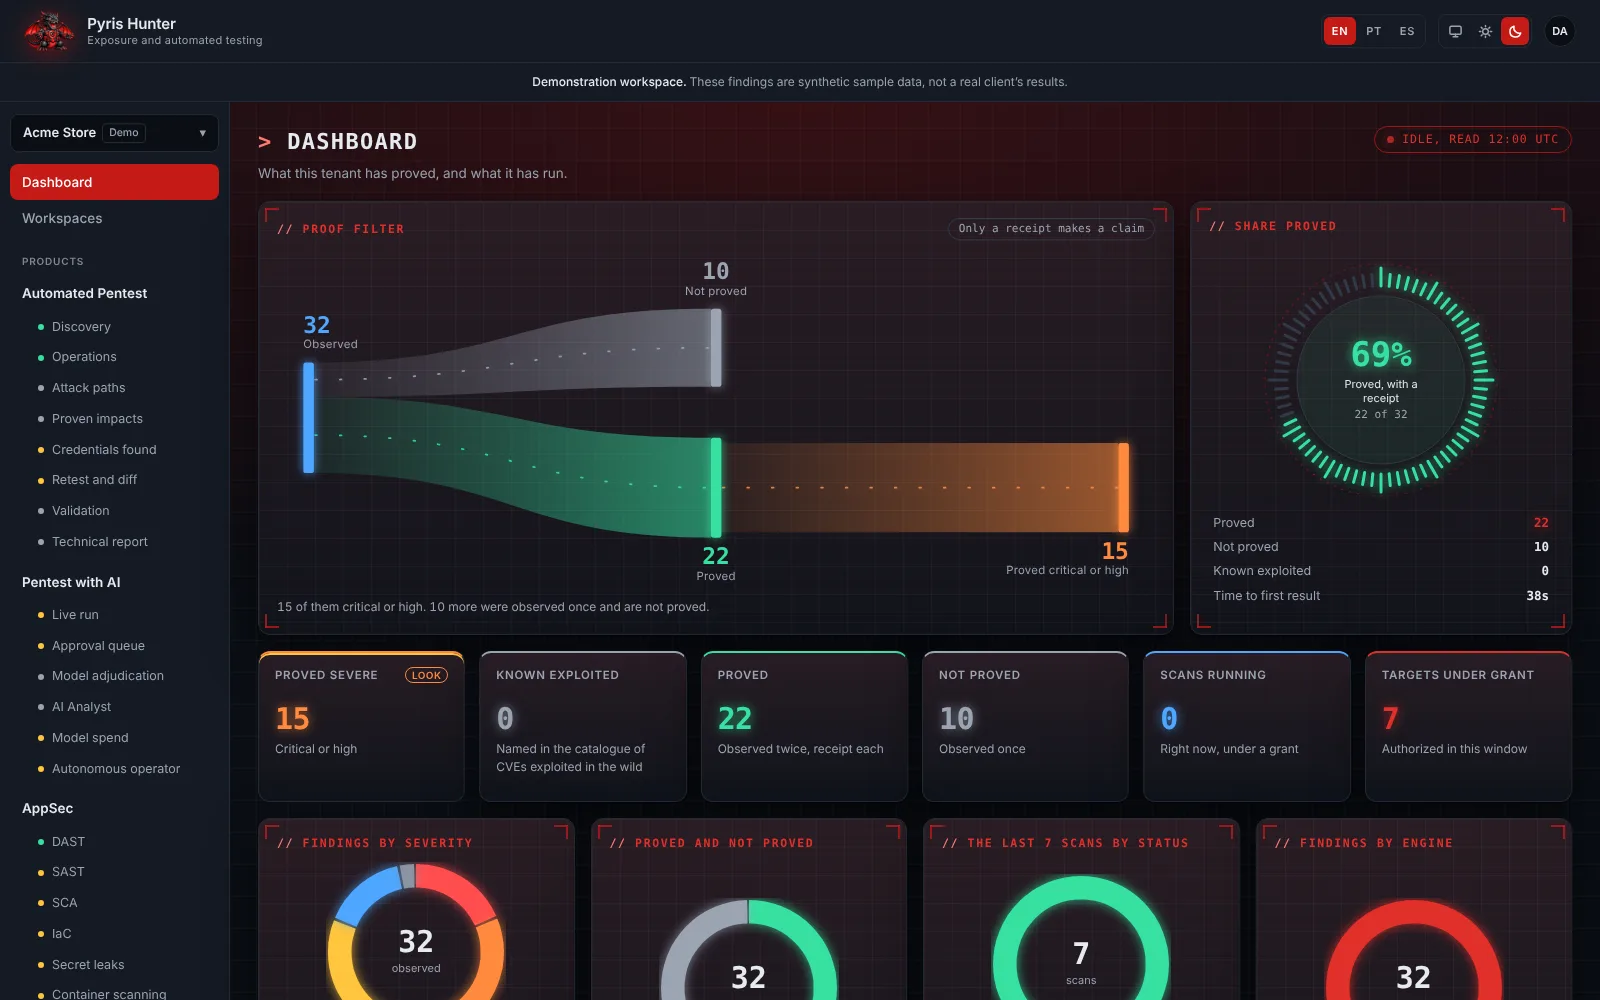
Pyris Hunter
Automated pentest, AI pentest, AppSec and API Security, with proof behind every finding.
Test your attack surface the way an attacker would, every day: automated pentest, AI-driven pentest with human approval, end-to-end AppSec (DAST, SAST, SCA, RASP and Threat Modeling) and API security. Every confirmed finding arrives with the request and response that prove it, never a guess.
- Continuous automated pentest
- AI pentest, with human approval
- AppSec: DAST, SAST/SCA/RASP and Threat Modeling
- API Security with BOLA, BFLA and IDOR proved
Pyris Intelligence
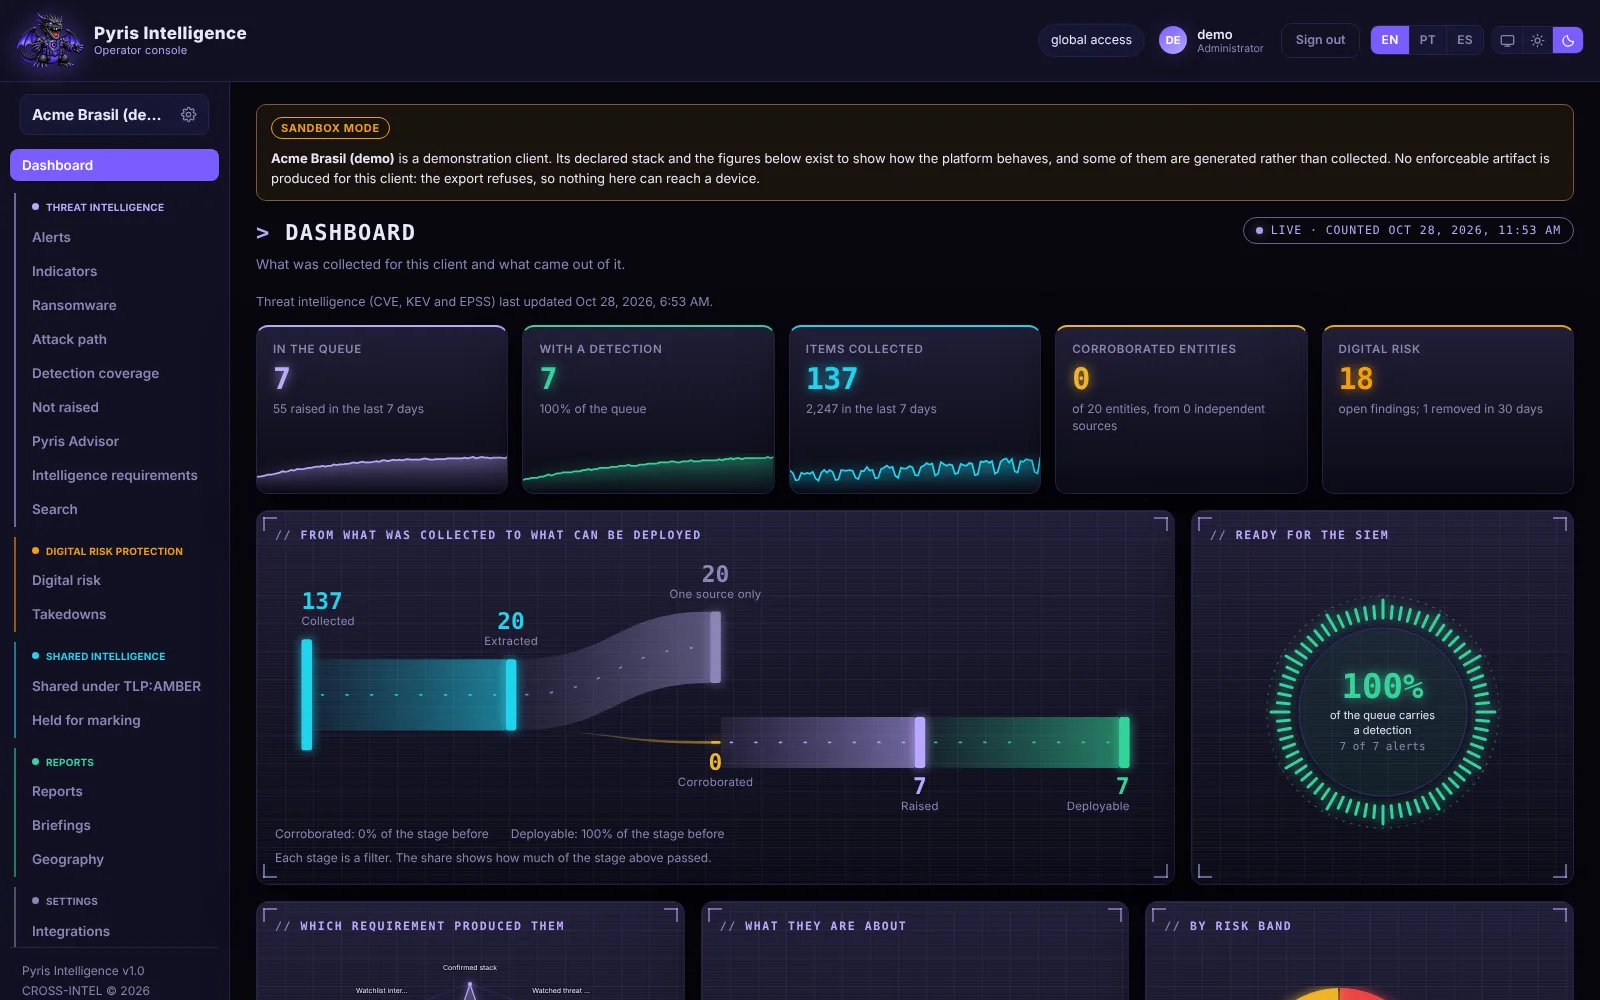
Corroborated intelligence that ships as a detection.
Cyber Threat Intelligence fused with Digital Risk Protection. It ingests and corroborates threat sources across independent origins, matches them to your stack and your people, and produces a detection ready for your SIEM.
- Multi source, corroborated intelligence
- Matched to your technology and people
- Detections ready for your SIEM (KQL, SPL)
- ATT&CK mapping, STIX, MISP and TAXII
Pyris Identity
The identities you have, ranked by real exposure.
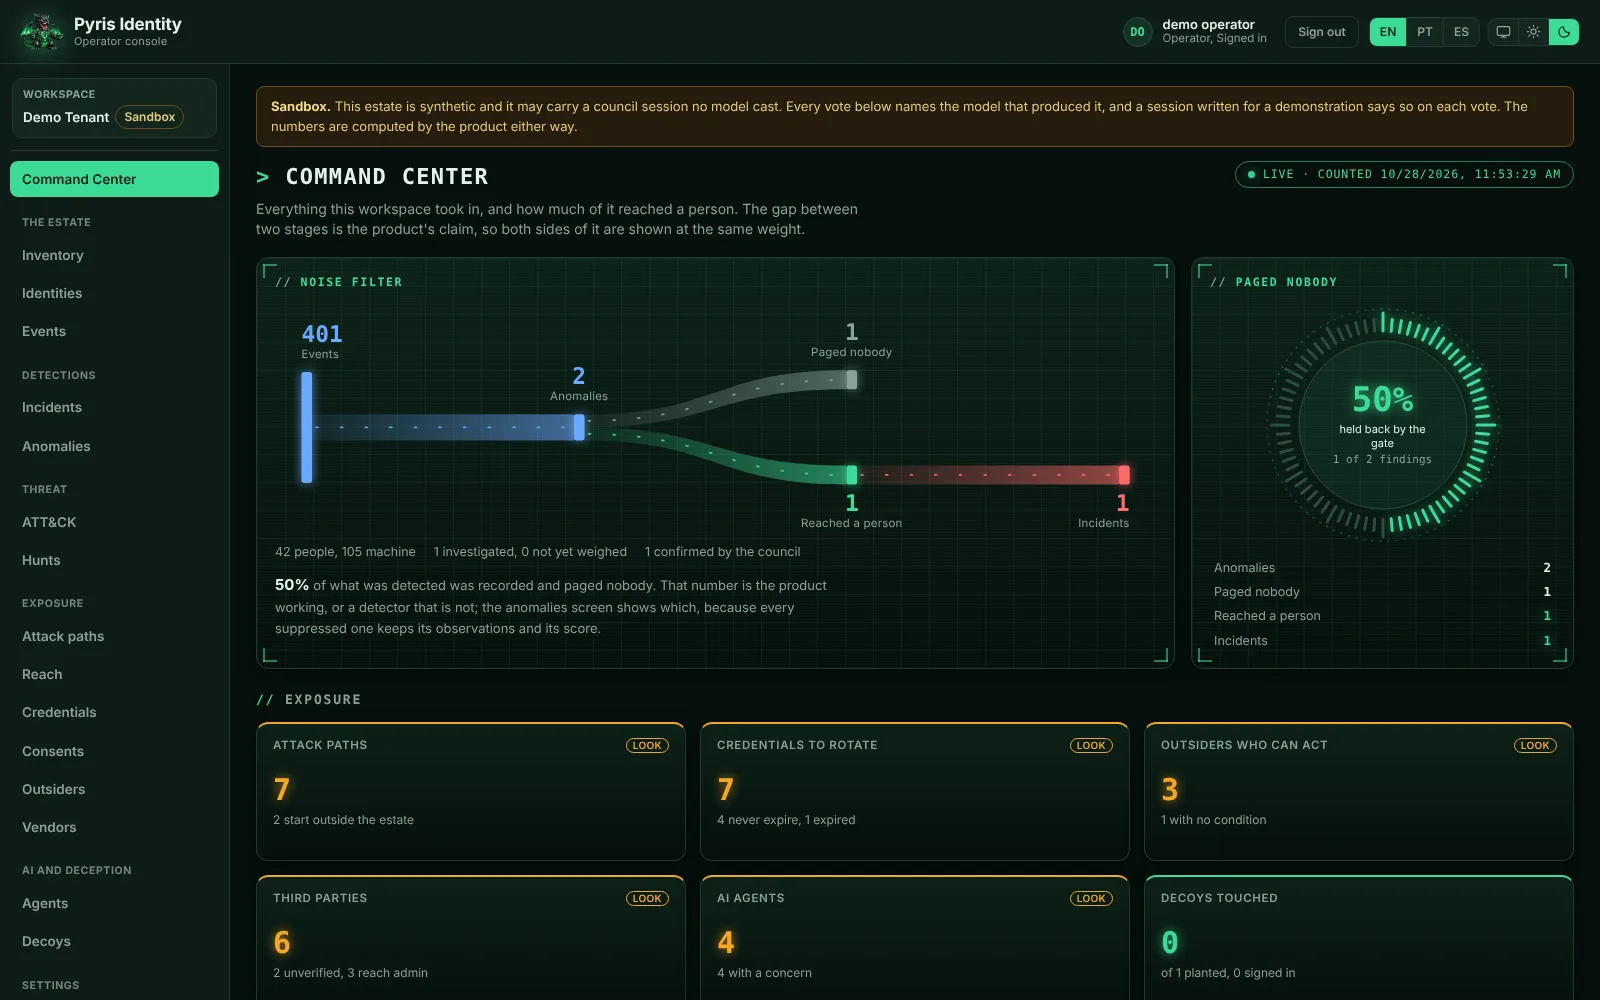
Identity security posture management across your directories. It builds a live inventory, scores privilege, ownership and credential exposure, detects anomalies behind a deterministic gate, and gives a managed SOC a single operator view.
- Live identity inventory
- Privilege, ownership and credential-exposure scoring
- Anomaly detection with a deterministic gate
- Managed-SOC operator view
Pyris Shield
An operations layer on the SOC you already own.
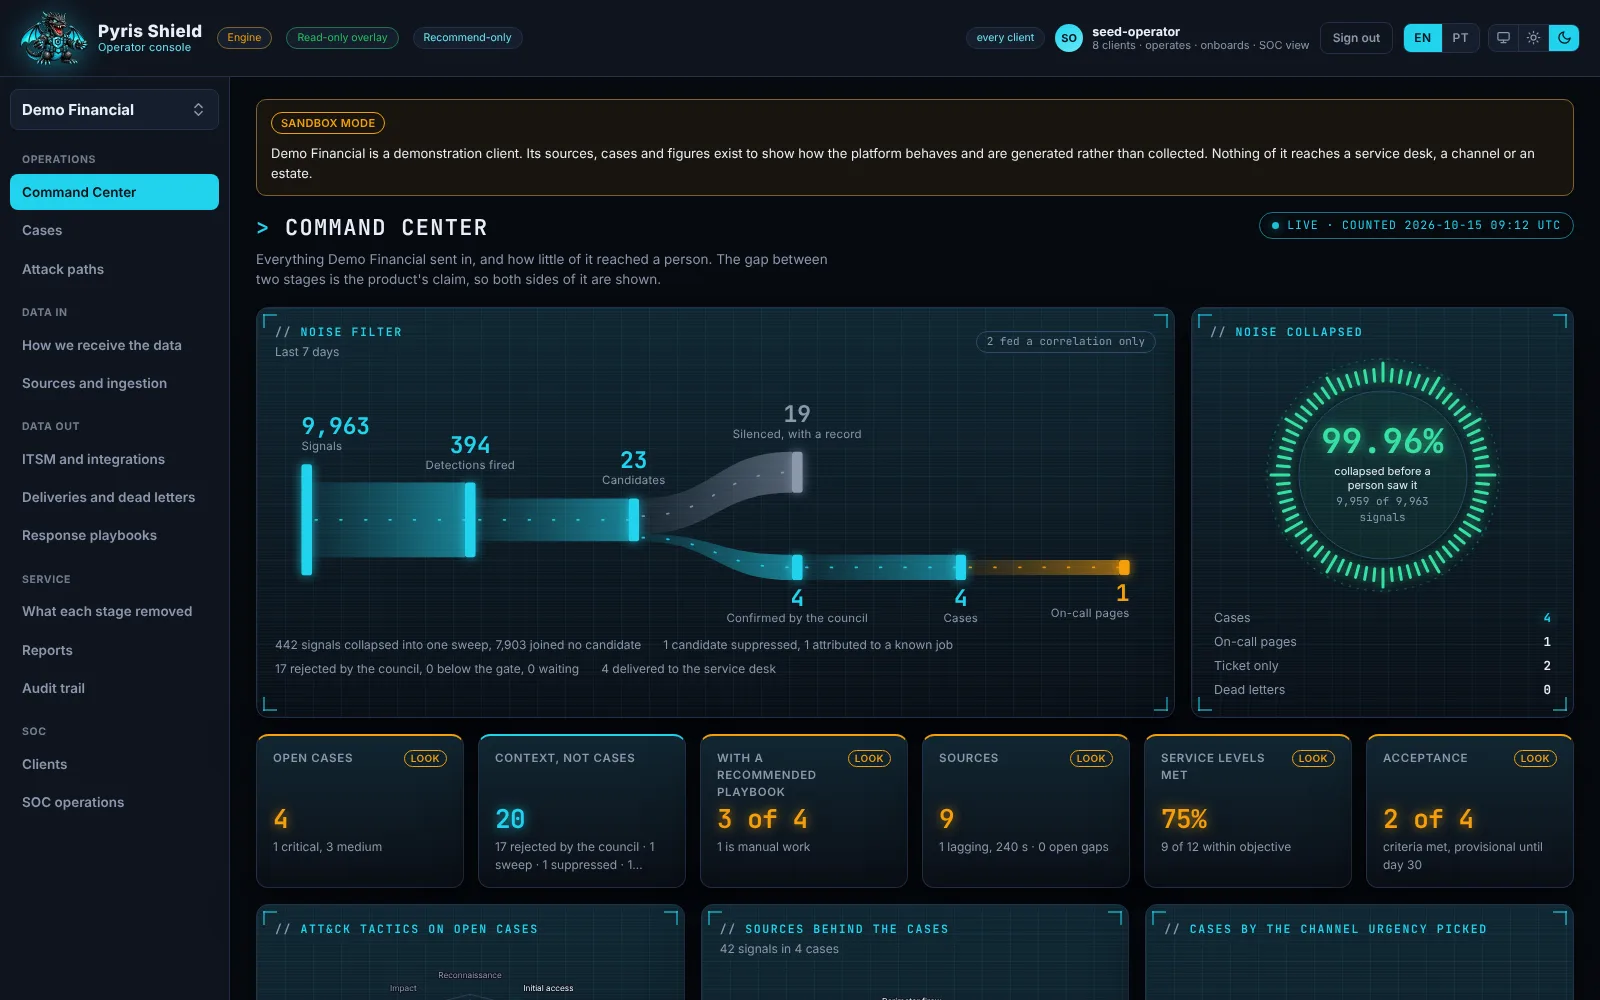
A co-managed detection and response layer that reads a read-only, OCSF normalized stream from your existing SOC or SIEM. It correlates, triages and investigates, and delivers the evidence straight into your service desk.
- Co-managed overlay, never your log lake
- OCSF normalized detection
- Evidence delivered to your ITSM
- Council quorum before any verdict
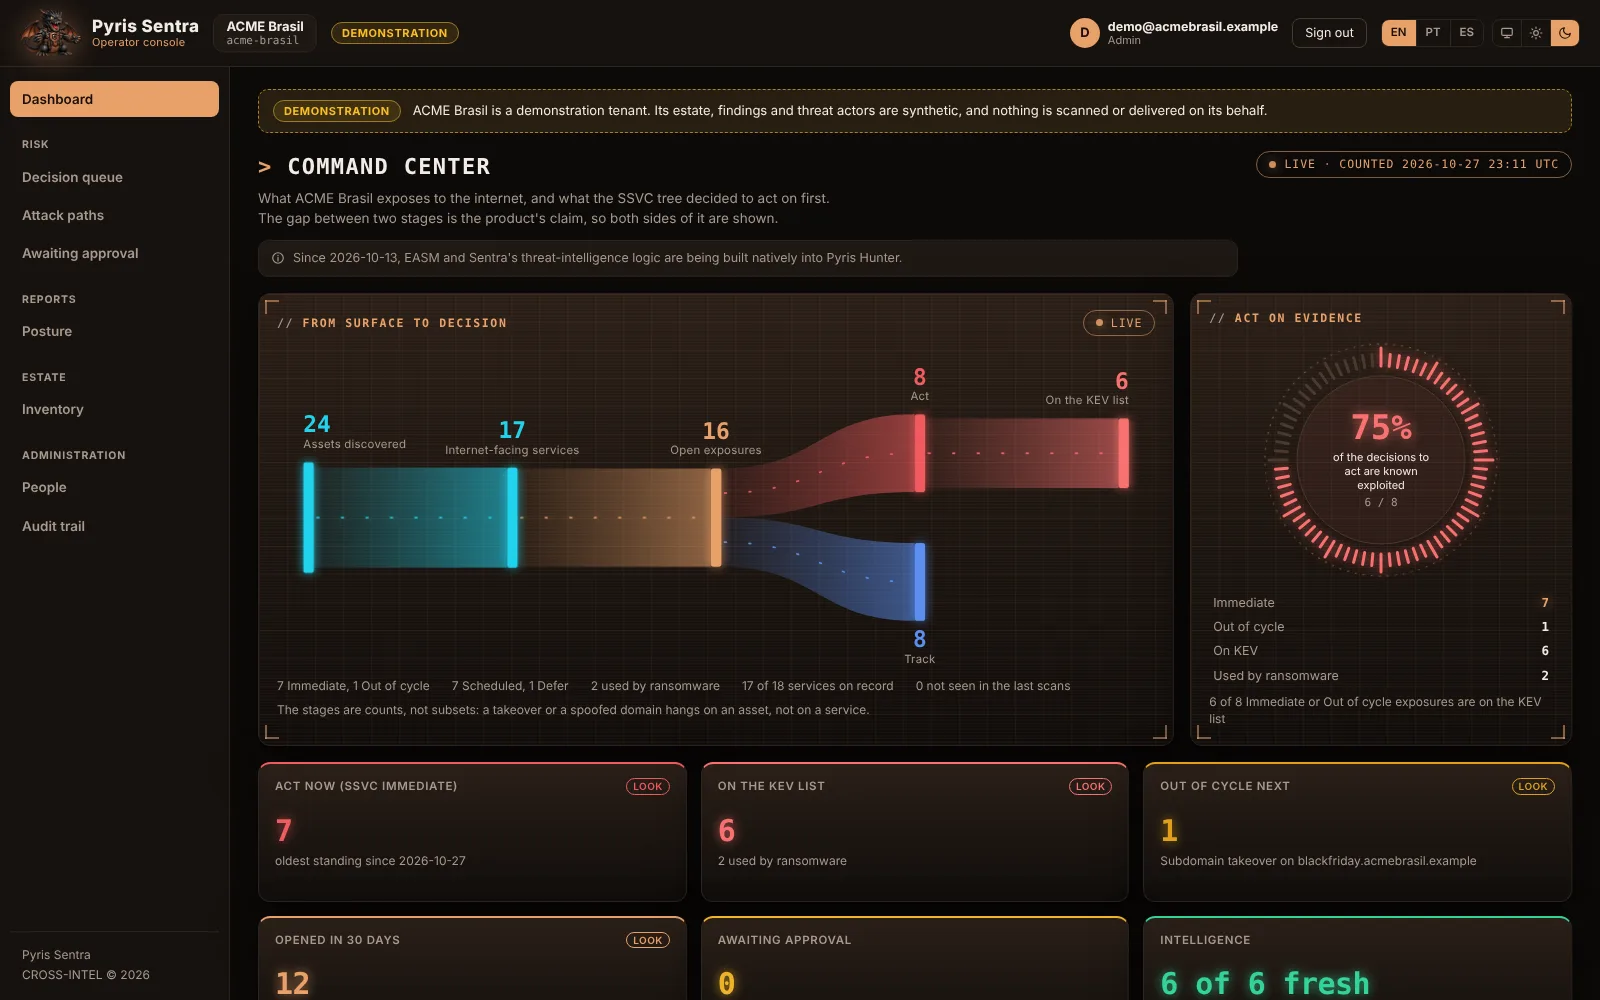
Pyris Sentra
See everything you expose to the internet, before an attacker does.
Continuous External Attack Surface Management. It discovers your internet facing assets (domains, subdomains, hosts, ports, services and technologies), tracks how that surface changes over time, and prioritizes each exposure so your team fixes what matters first.
- Continuous discovery of internet facing assets
- Subdomains, ports, services and technology fingerprint
- Change detection as your attack surface evolves
- Explainable, risk based prioritization
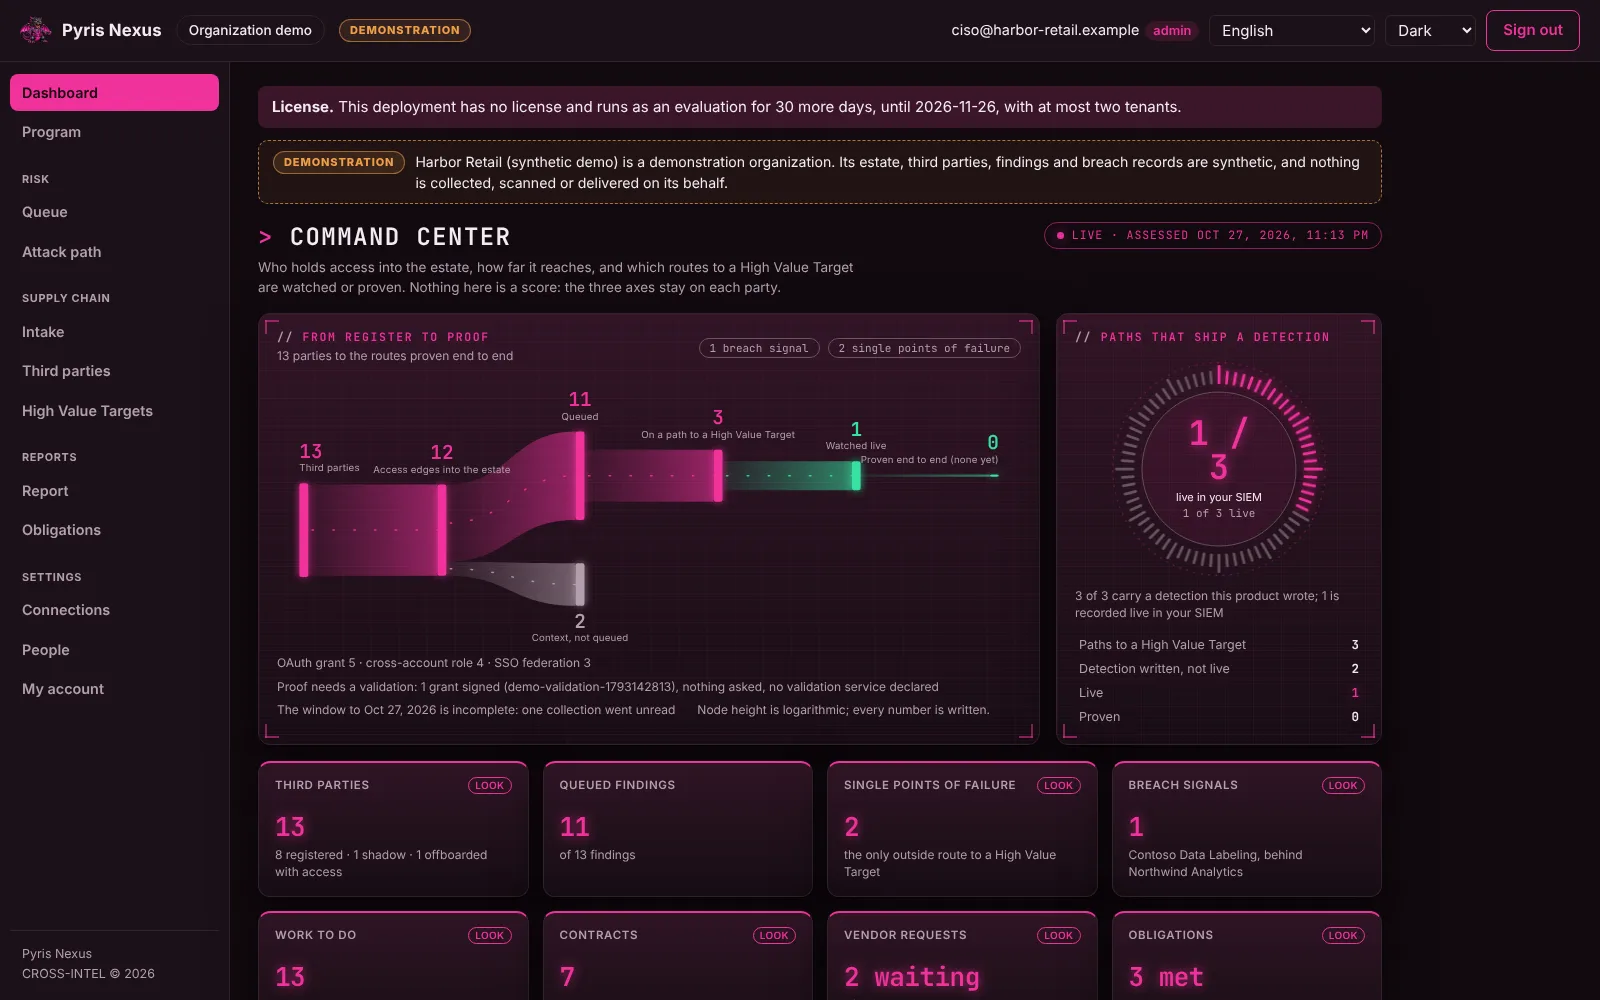
Pyris Nexus
Third-party risk, traced to the High Value Target.
Third-Party Risk Management and supply-chain security that does not rate a vendor in isolation. It maps the live access each third party holds into your estate, traces the path a compromise would take to a High Value Target, scores by operational resilience, and ships a detection with every finding.
- Third and nth-party inventory with tiering
- Live access discovery: OAuth, cross-account cloud roles, SSO
- Attack Path and blast radius to your High Value Targets
- Exposure, blast radius and resilience impact, never blended
Not sure where to start?
Tell us your attack surface and your stack. We will map the right combination of the Pyris platform to it.
Book a Call