Pyris Intelligence · Threat Intelligence + Digital Risk
Intelligence that becomes detection.
Cyber Threat Intelligence and Digital Risk Protection in a single platform
Threats corroborated by independent sources, filtered by the reality of your environment and delivered with the rule ready for your SIEM.
Corroborated?
Seen in truly independent sources, not in copies of the same press release.
Relevant?
Matched against your stack, sector, geography, brand and protected people.
Moving?
Velocity across 1 hour to 7 day windows, plus KEV and EPSS for CVEs.
Actionable?
A Sigma rule rendered to your SIEM dialect, ready to deploy.
Real console screens
Dashboard
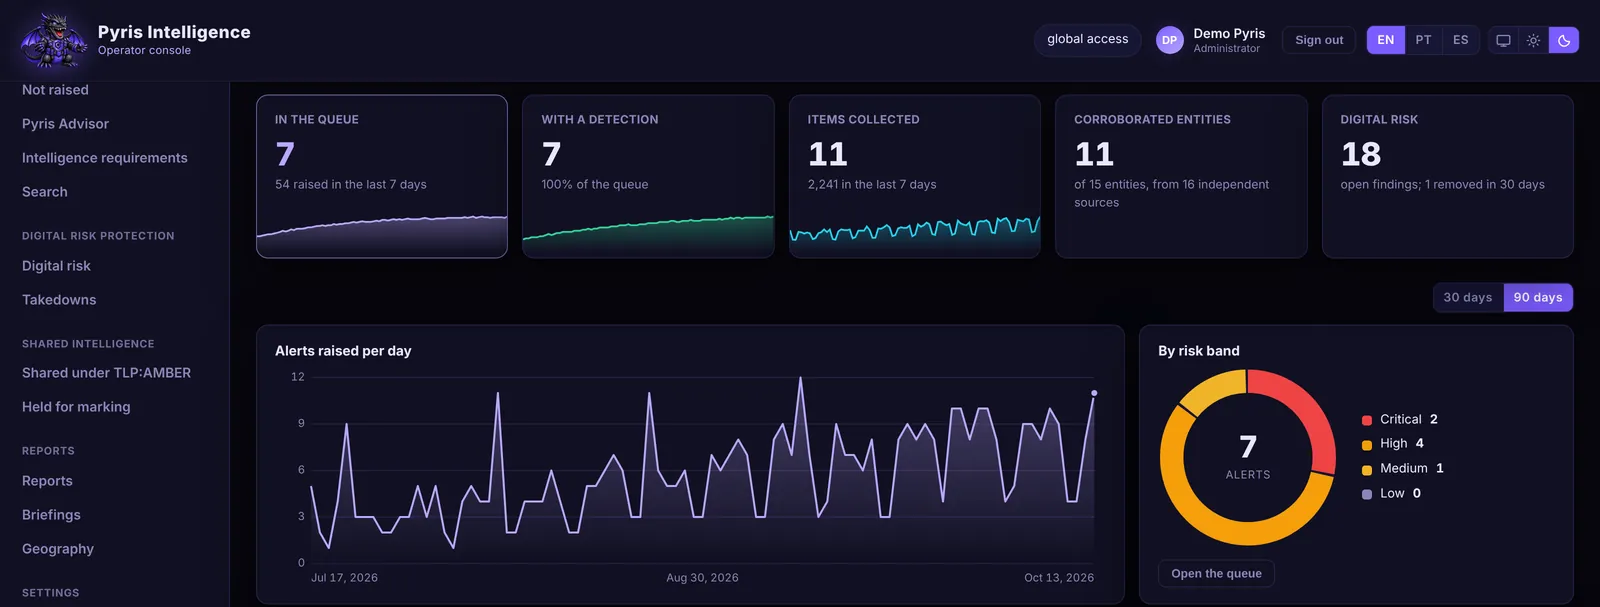
One screen with what a security leader needs to know: the alert queue, what already carries a detection, the volume collected, what was corroborated and the open digital risk findings. Below, alerts per day over 30 or 90 days, the breakdown by risk band and the map of attack paths targeting the customer.
What sells
Attack Path
The complete attack chain, in kill chain order: who could come after the customer, through which MITRE ATT&CK techniques, opened by which of the customer's own exposures, and landing on which assets.
- Every link says how it is known: observed in collection, documented by ATT&CK, enabled by a finding or exploiting a KEV vulnerability
- It shows which exposure to close first, and it is the picture a security leader takes to the board
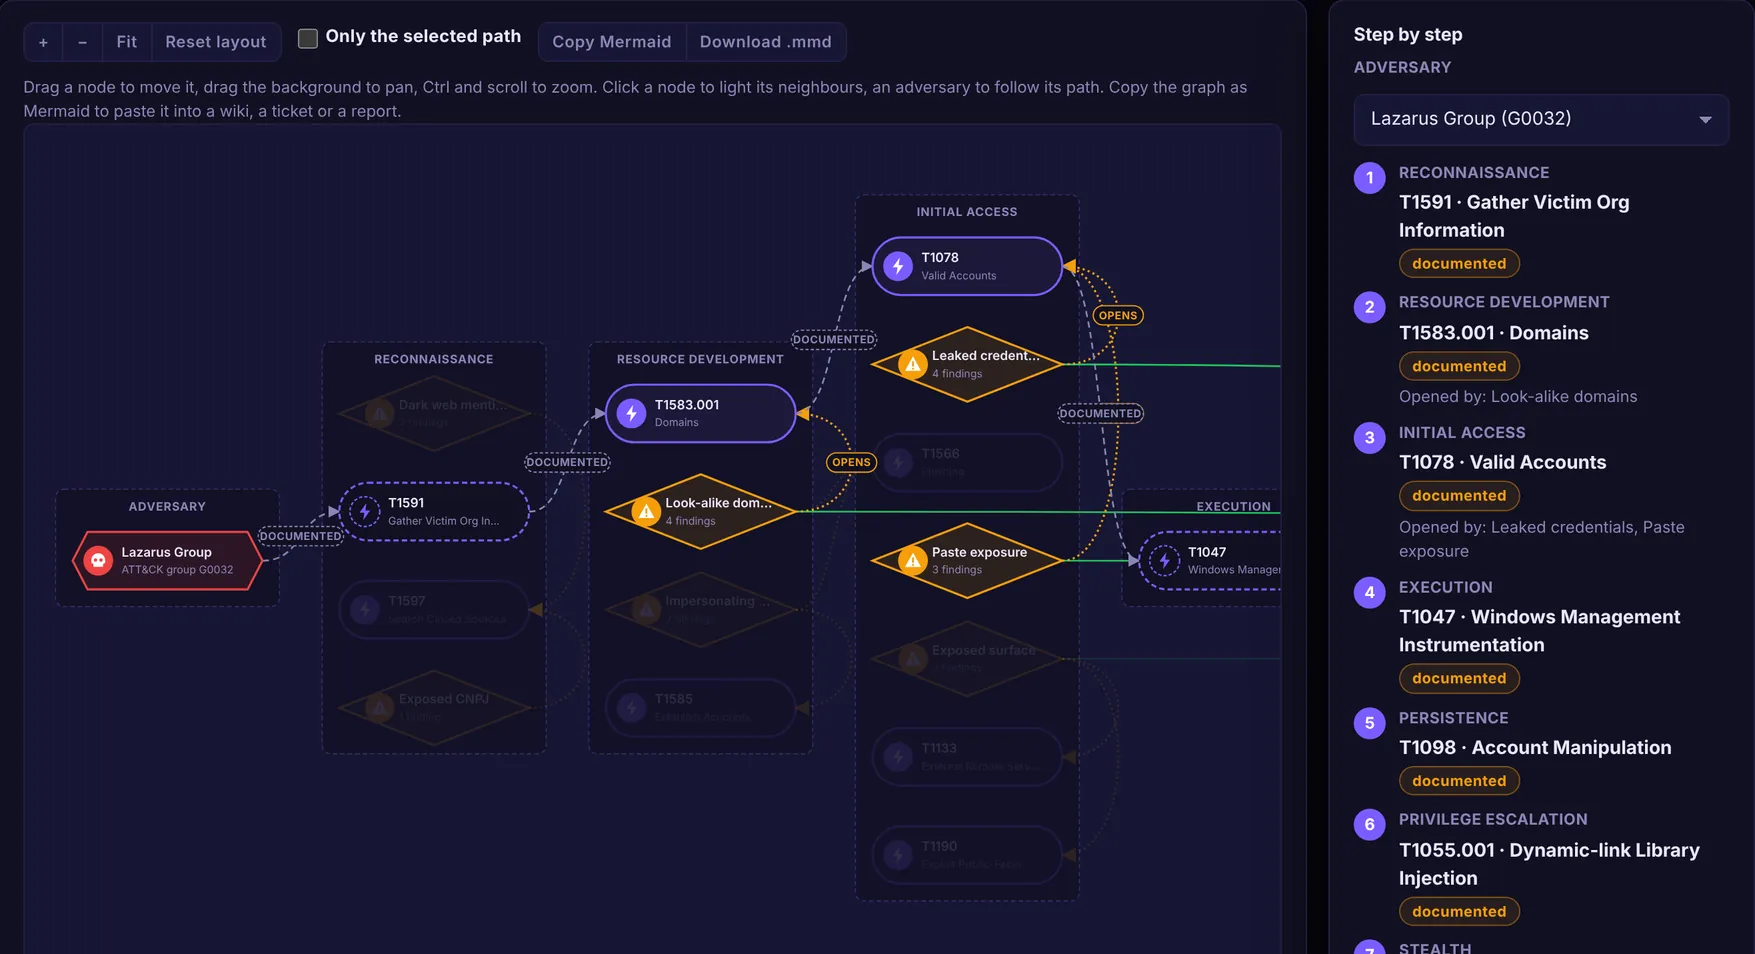
Real console screens in demonstration mode, with the fictitious customer ACME Brasil.
See Pyris Intelligence on your own environment
A 30 minute walkthrough with our specialists, using a demonstration tenant and your own use cases.
What it is
Pyris Intelligence is a Cyber Threat Intelligence platform fused with Digital Risk Protection. It continuously ingests open and commercial threat sources, corroborates every claim across independent origins, matches what it learns against each customer's technology stack, brand and protected people, and delivers a detection ready for the SIEM, not just another digest.
Why it is different
Every alert answers four questions at once. Anything that cannot answer all four is context, and it never wakes anyone up at three in the morning.
Outcomes
- A queue ranked by confidence, relevance and trend
- Transparent evidence, no black box score
- Multi tenant operation built for MSSPs
Core capabilities
- Native collection in Portuguese and Spanish, with a curated catalog of Brazilian, LATAM and Iberian sources
- Intelligence spine with CVE, EPSS, CISA KEV and threat actors, refreshed daily
- Deterministic detections in Sigma, rendered to Microsoft Sentinel (KQL) and Splunk (SPL)
- Digital Risk Protection: brand, executives, look-alike domains, leaked credentials and dark web
- MITRE ATT&CK mapping and a per customer Attack Path graph
- Distribution over STIX, MISP, TAXII and blocklists
Innovation
What sets it apart
Ready detections
Sigma as the canonical form, delivered in KQL or SPL to match the customer's SIEM.
Managed takedown
Detection, evidence package, notification, follow up and confirmed removal.
Reports
For any period, in PDF, Word, CSV and Markdown, built from the same data as the screens.
Agent and Agentless
Agentless in the cloud with nothing to install, or an Agent collector inside the perimeter, air-gapped included.
Benefits
Less noise, more signal
Fifteen outlets repeating the same press release count as a single source. Analysts get what matters.
Relevant to your environment
Scored against the confirmed stack, sector, geography and protected people. If it does not touch you, it is not an alert.
From alert to detection
Every alert carries its own rule, in your SIEM dialect, with a complete and auditable evidence trail.
Brazil lens
Global indicators filtered by what targets Brazil: .br domains, and impersonated banks, Pix and federal services.
Built for
Deployment
Operating modes
Request a demo
Want to see Pyris Intelligence in action?
Tell us a little about your environment and a specialist will reach out within one business day to schedule a personalized demo.
- Live walkthrough of the Dashboard and Attack Path
- Mapping to your use cases and compliance needs
- Deployment options: SaaS, on-premises or air-gapped