Pyris Hunter · Offensive Security Platform
Real attacks. Proof in every finding.
Automated pentesting, DAST, API security and Red Team in a single platform
Agent and Agentless, across the external and the internal estate: continuous offensive testing, with a receipt for every finding.
Authorized
No action without a signed engagement. Scope is enforced by the platform itself.
Confirmed
Reproduction and validation separate the potential from the confirmed.
With a receipt
Every finding carries the real request and response that prove it.
Readable
Dashboards and reports a non technical leader understands.
Real console screens
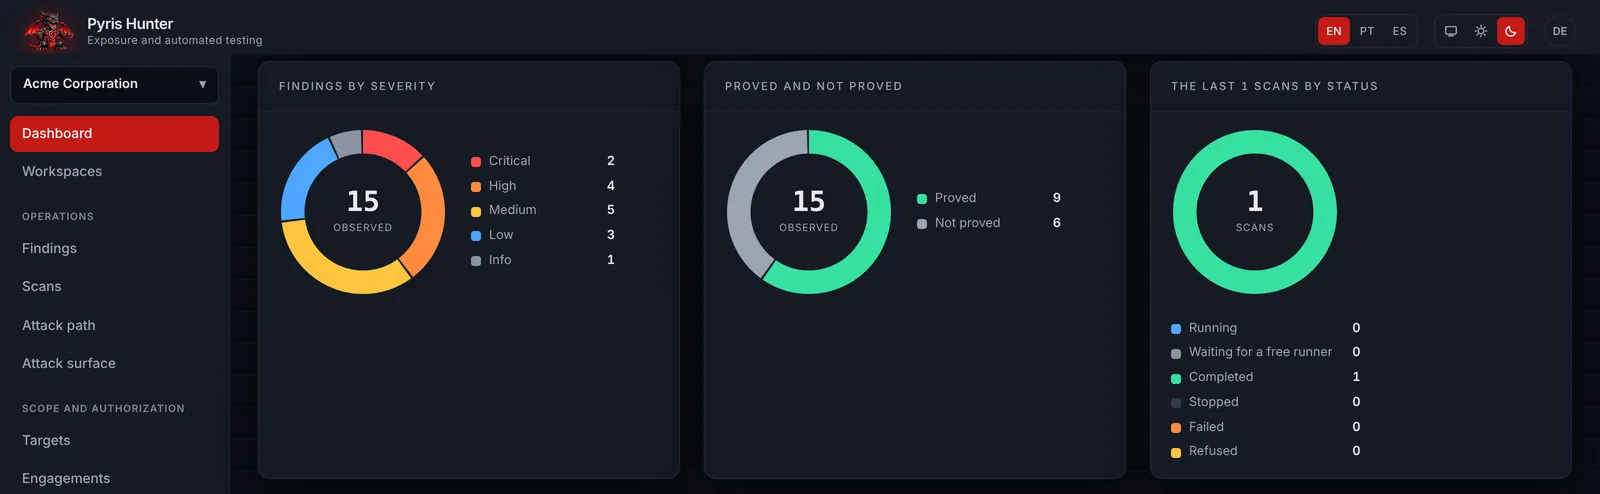
Dashboard
The customer's posture in charts a leader reads at a glance: findings by severity, proved and not proved, and scans by status. Every number opens the finding and the receipt behind it.
What sells
Attack Path
The attack chains Pyris Hunter proved, drawn as an interactive graph in three lanes (external, internal estate and cloud): from a host that takes input from the internet to an internal asset or a cloud role, step by step, with the MITRE ATT&CK technique on every link.
- The headline is what a chain proved, never a count
- Every step says what it produced and why it is exactly what the next one consumed
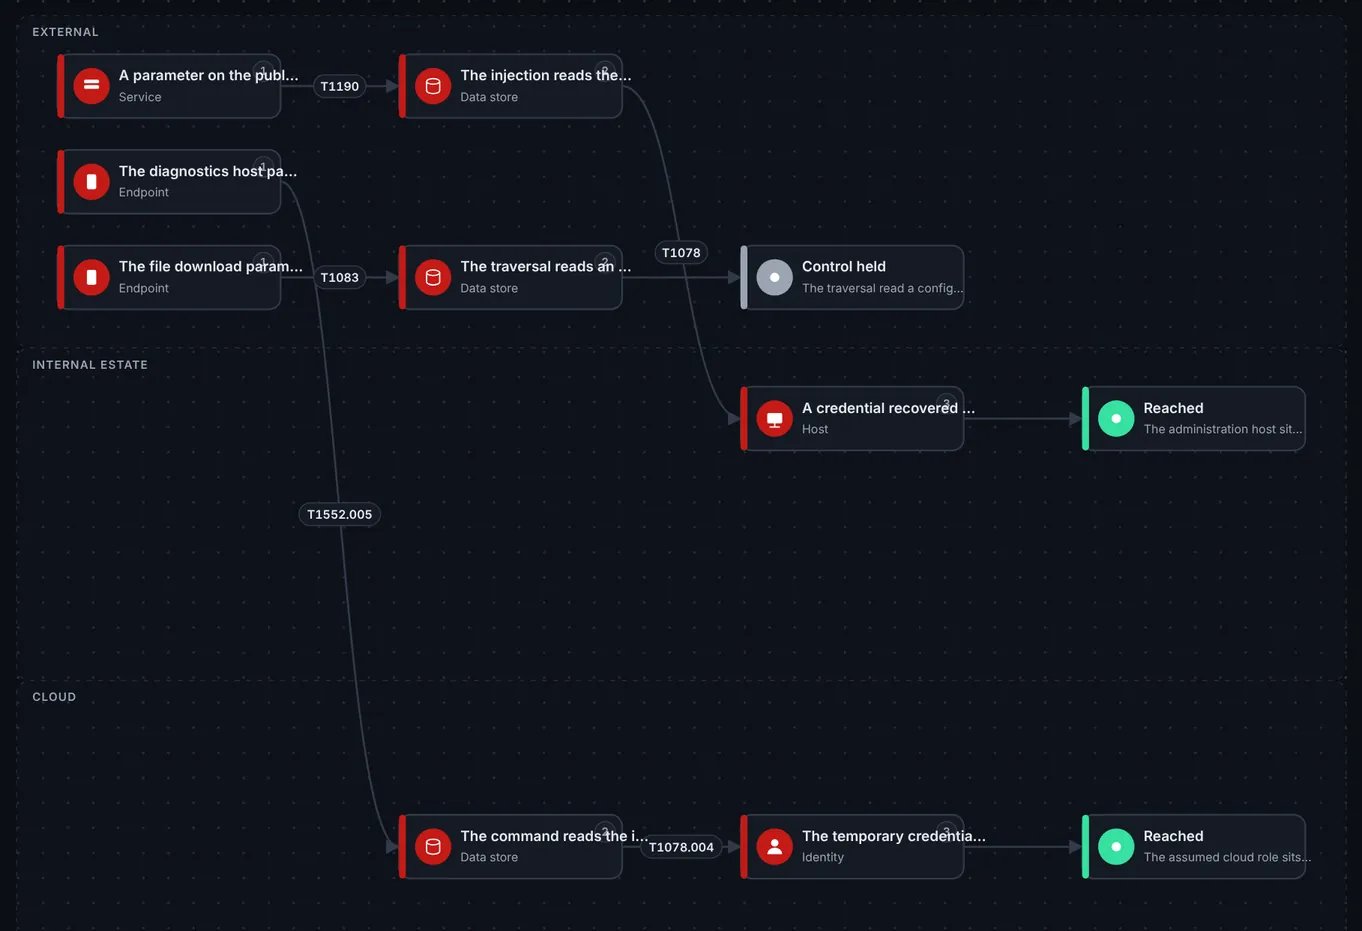
Real console screens in a demonstration workspace, with fictitious data.
See Pyris Hunter on your own environment
A 30 minute walkthrough with our specialists, using a demonstration tenant and your own use cases.
What it is
Pyris Hunter is an offensive security platform for continuous exposure visibility and automated offensive testing: automated pentesting, vulnerability scanning, DAST, API security and Red Team operations. Many engines run behind one contract and share discovery, deduplication, reproduction, correlation and scoring. Everything runs under a pentest engagement authorized by contract.
Why it is different
False positives are the enemy. A finding reaches the screen as confirmed only when it comes with its proof, and that proof is what the customer buys.
Outcomes
- Confirmed findings, each with its receipt
- A ranked queue the business understands
- Technical and executive PDF reports
- Traffic your blue team can recognize
Core capabilities
- Discovery of subdomains, ports, services, versions, technologies, content and API specifications
- DAST: SQL injection, reflected and stored XSS, SSTI, XXE, command injection, path traversal and upload
- Authenticated and API testing: IDOR, BOLA and BFLA proven by the authorized and unauthorized request pair
- Blind classes confirmed through out-of-band interaction, such as blind SSRF and blind command injection
- Exposed services: unauthenticated databases, directories, legacy protocols and subdomain takeover
- AI and MCP attack surface, including indirect prompt injection
Innovation
What sets it apart
Post access Red Team
Persistence, lateral movement and adversary emulation, with scope at the implant, expiry and a kill switch.
Continuous EASM
Continuous discovery and monitoring of the external surface, with built in threat intelligence.
AI Operator
A planner that reads the graph and the findings and chooses the next test, with human approval.
Agent and Agentless
Both modes cover the external and the internal estate: nothing to install, or a light agent inside the environment, including assumed breach.
Graded safe mode
From read only to controlled exploitation, with the ceiling set per engagement.
Emergency stop
The customer halts any scan, and the platform shows that it stopped.
Retest and MCP
The developer's coding agent reads the finding and requests the retest of the fix.
AI second opinion
Critical and high findings can be adjudicated by a model, with consent.
Benefits
Fast and continuous
On demand and scheduled scans, worst exposure first and alerts when the surface changes.
No noise
An engine ships only after proving it fires on the vulnerable target and stays quiet on the clean one.
Safe by design
Graded safe mode, enforced scope and an emergency stop that proves it stopped.
Grey box
Code findings (Drogonsec SAST and SCA) joined with live confirmation.
Built for
Deployment
Operating modes
Request a demo
Want to see Pyris Hunter in action?
Tell us a little about your environment and a specialist will reach out within one business day to schedule a personalized demo.
- Live walkthrough of the Dashboard and Attack Path
- Mapping to your use cases and compliance needs
- Deployment options: SaaS, on-premises or air-gapped