Pyris Nexus · Third-Party Risk + Supply Chain
Not a grade. A path.
Third-party risk management and supply-chain security
The real access each vendor holds into your estate, the attack path to your High Value Target and what stops if that link falls.
Connected?
OAuth, API, cross-account role, SSO federation: the live access and its privilege.
How far?
The blast radius: what that access reaches across the chain, up to the High Value Target.
Exploitable?
A path proven with a receipt, not just possible.
What breaks?
Resilience impact: business service, concentration and single point of failure.
Real console screens
Dashboard
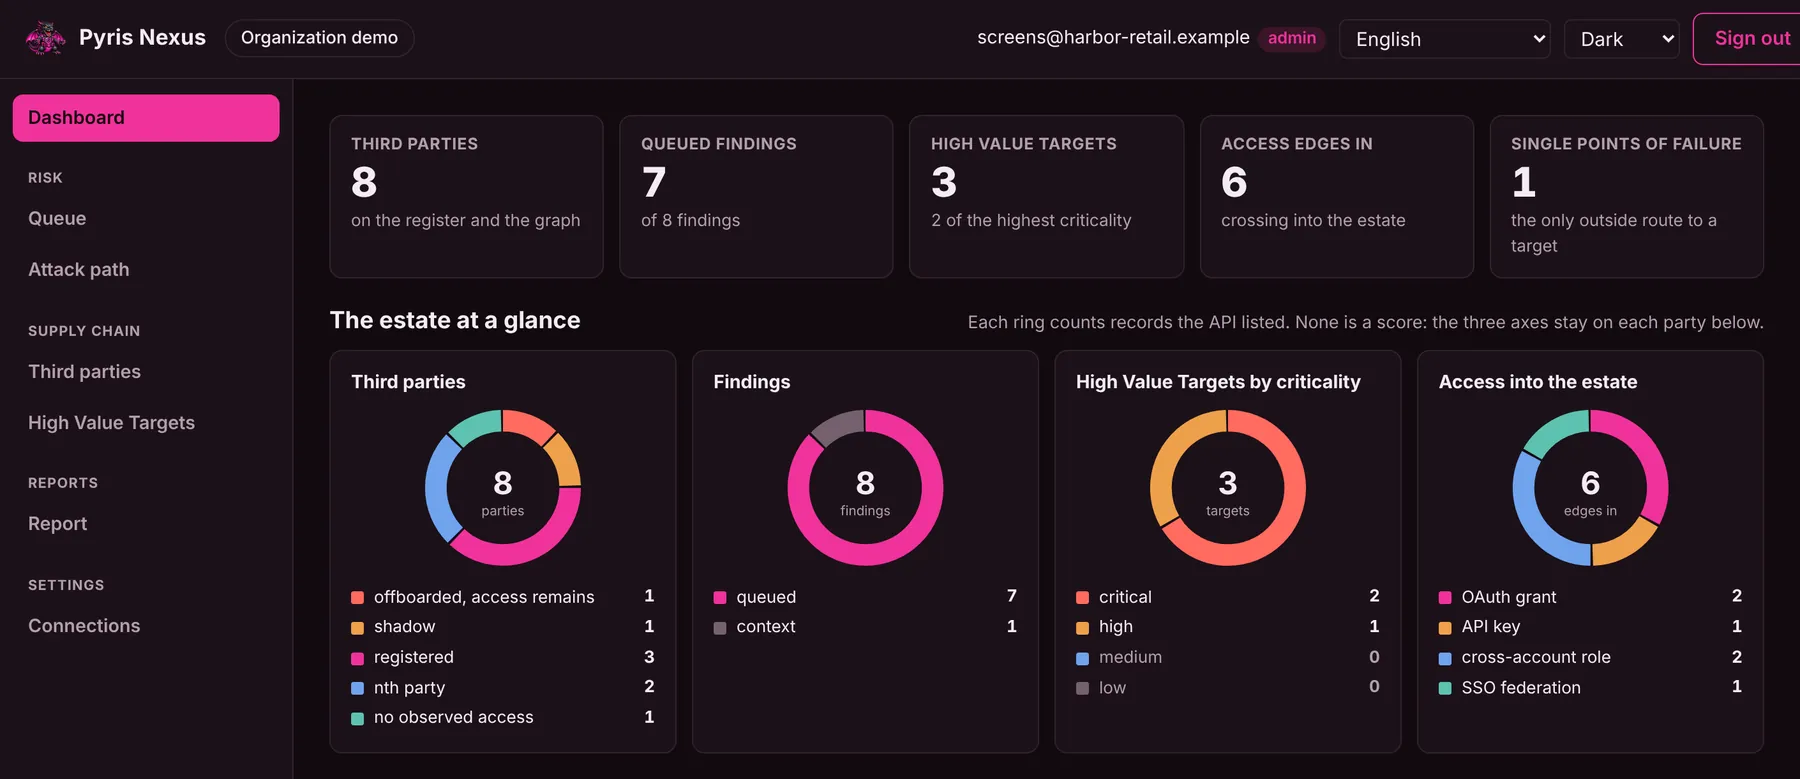
The new console, in the Pyris family layout: a sidebar by section and a Dashboard with the key figures (third parties, queued findings, High Value Targets, access edges in and single points of failure) and pie charts by status, criticality and access type.
What sells
Attack Path
The path an attacker takes through the supply chain: from the vendor (or the vendor's vendor) through the access it holds to the High Value Target and the business service that stops.
- Every link says how it is known and whether a receipt proves it
- It shows the single point of failure every route crosses
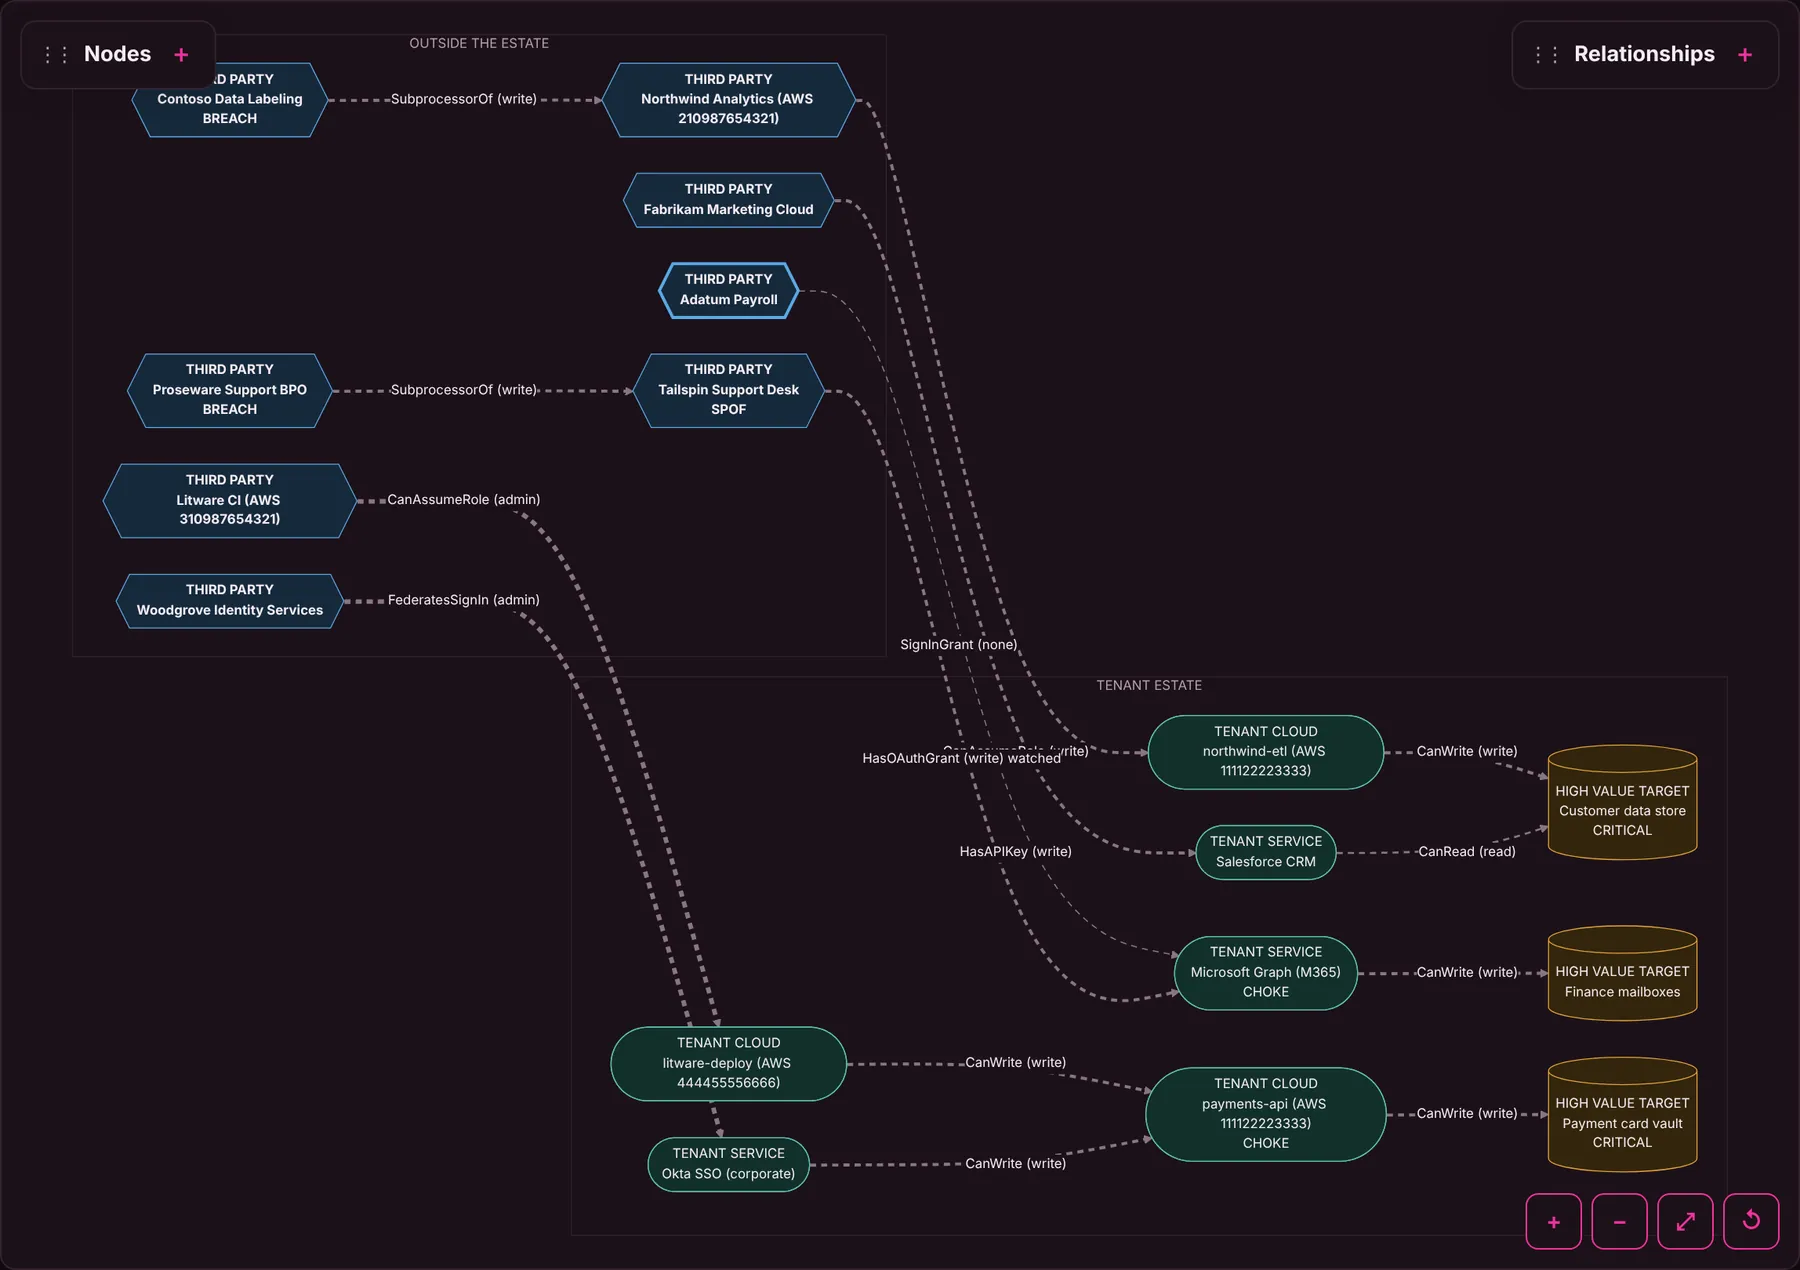
Real console screens with the demonstration tenant, with fictitious data.
See Pyris Nexus on your own environment
A 30 minute walkthrough with our specialists, using a demonstration tenant and your own use cases.
What it is
Pyris Nexus is a TPCRM and supply-chain security platform. It does not rate a vendor in isolation: it draws the live connective tissue between the customer and its third parties, fourth parties and cloud services, and it produces a decision. Which path an attacker takes through the supply chain to a High Value Target, what falls if a link is breached and what to fix first. Operational resilience is the scoring model.
Why it is different
A vendor with a bad grade and no access is context. A vendor with a good grade and a write role in production is the top of the queue.
Outcomes
- A queue by real risk, not by grade
- A decision explained axis by axis
- Evidence ready for DORA, NIS2 and ISO 27036
- Multi tenant for MSSPs and consultancies
Core capabilities
- Access discovery: OAuth and API grants in M365 and Google, cross-account AWS roles and SSO federation
- Outside-in rating and third-party cloud posture (AWS and Entra ID), with no cooperation required
- Declared fourth and fifth parties, with the tier derived from the real route of the access
- Breach signals per company, never per person, with built in threat intelligence
- Concentration and single point of failure: who is the only route to each High Value Target
- Offensive proof of a path by Pyris Hunter, under the customer's authorization
Innovation
What sets it apart
Agent and Agentless
Agentless from the outside in and over API; an Agent collector inside your estate reads the inner side of every access.
Detection per path
A Sigma rule per access, in the SIEM's dialect, with coverage tracked.
AI questionnaires
Reads the SOC 2 and the subprocessor page, drafts against evidence and a person signs.
What-if simulation
Remove an access or a vendor and see who becomes the only route.
Continuous change
The graph is recollected and every change is sent by signed webhook.
Compliance
Mapping to SOC 2, ISO 27036, DORA and NIS2.
Integrations
Jira, ServiceNow, webhooks and OCSF out to the SIEM.
A proven method
Based on the book TPRM-Driven Supply Chain Cybersecurity, by Filipi Pires.
Benefits
The graph crosses the boundary
Ratings judge the vendor alone. Nexus maps the access it holds inside you.
Proof, not just a grade
A path is marked proven only with a receipt: exposure, breach or validation.
GRC and SOC together
Every path ships a Sigma detection in your SIEM's dialect.
What if?
Cut an access or drop a vendor and see the graph recomputed on the spot.
Built for
Deployment
Operating modes
Request a demo
Want to see Pyris Nexus in action?
Tell us a little about your environment and a specialist will reach out within one business day to schedule a personalized demo.
- Live walkthrough of the Dashboard and Attack Path
- Mapping to your use cases and compliance needs
- Deployment options: SaaS, on-premises or air-gapped