Pyris Sentra · External Attack Surface Management Platform
Not a score. A decision.
External attack surface management (EASM) fused with threat intelligence
It continuously discovers everything you expose to the internet, matches it against who is exploiting right now and says what to fix first, with a decision that explains itself.
Exploitable?
CVSS impact, CWE class and exploit maturity.
Exploited now?
CISA KEV, EPSS and active threat actor campaigns.
By whom?
Actors targeting your sector and their TTP overlap.
Does it hit you?
An asset confirmed as yours, reachable and critical to the business.
Real console screens
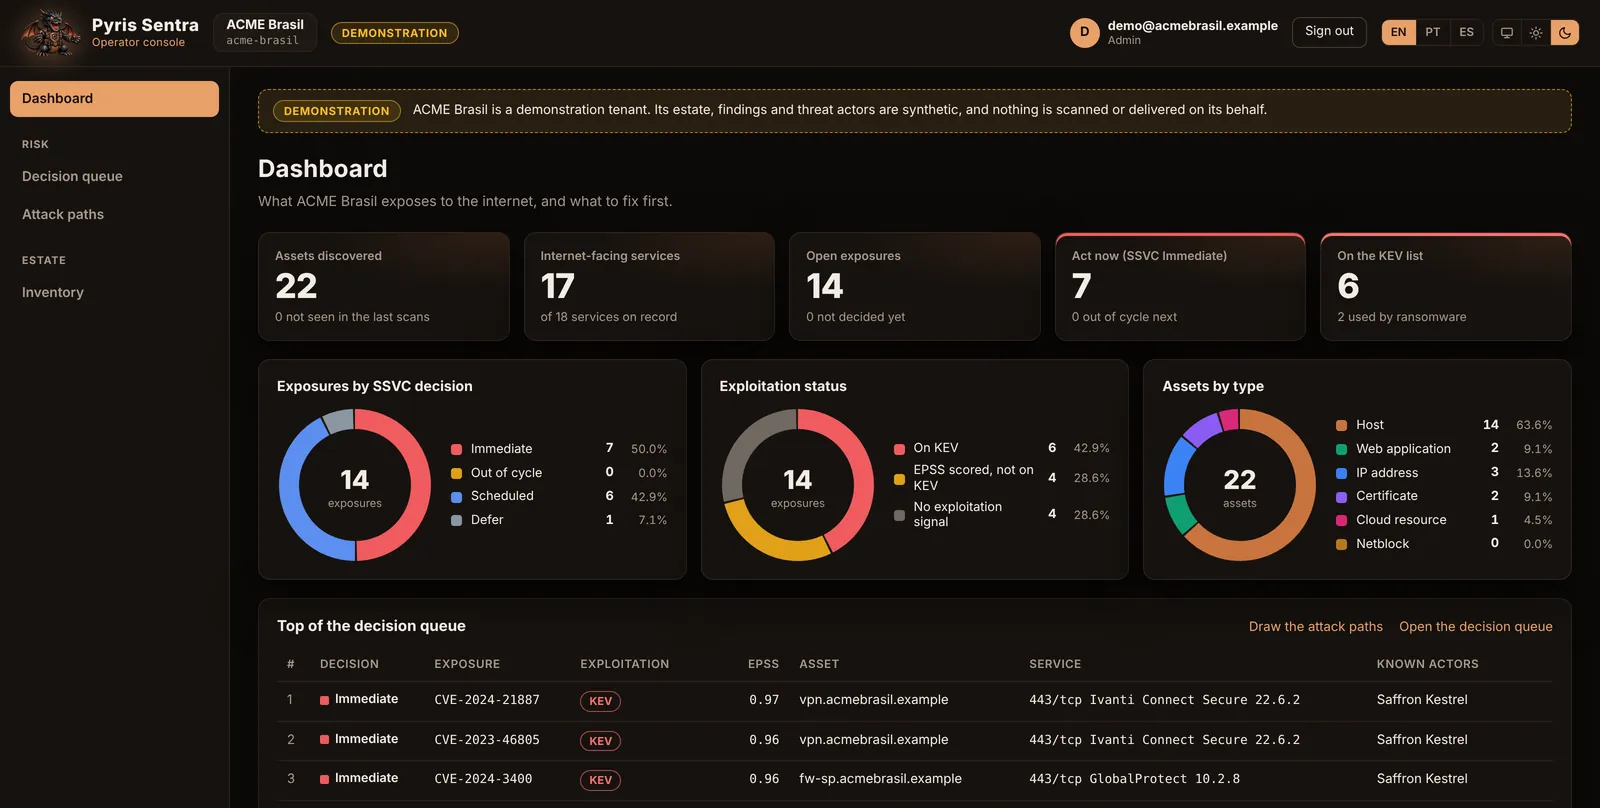
Dashboard
The external surface on one screen: assets discovered, internet services, open exposures, what to act on now and what is on KEV, with exposures by SSVC decision, assets by type, exploitation and the decision queue.
What sells
Attack Path
From the actor who is exploiting, through the vulnerability and the exposed service, to the asset hit, in decision queue order.
- In the demo: 15 paths, 3 actors and 6 KEV CVEs with EPSS above 0.94
- The path decided Act is what to fix today
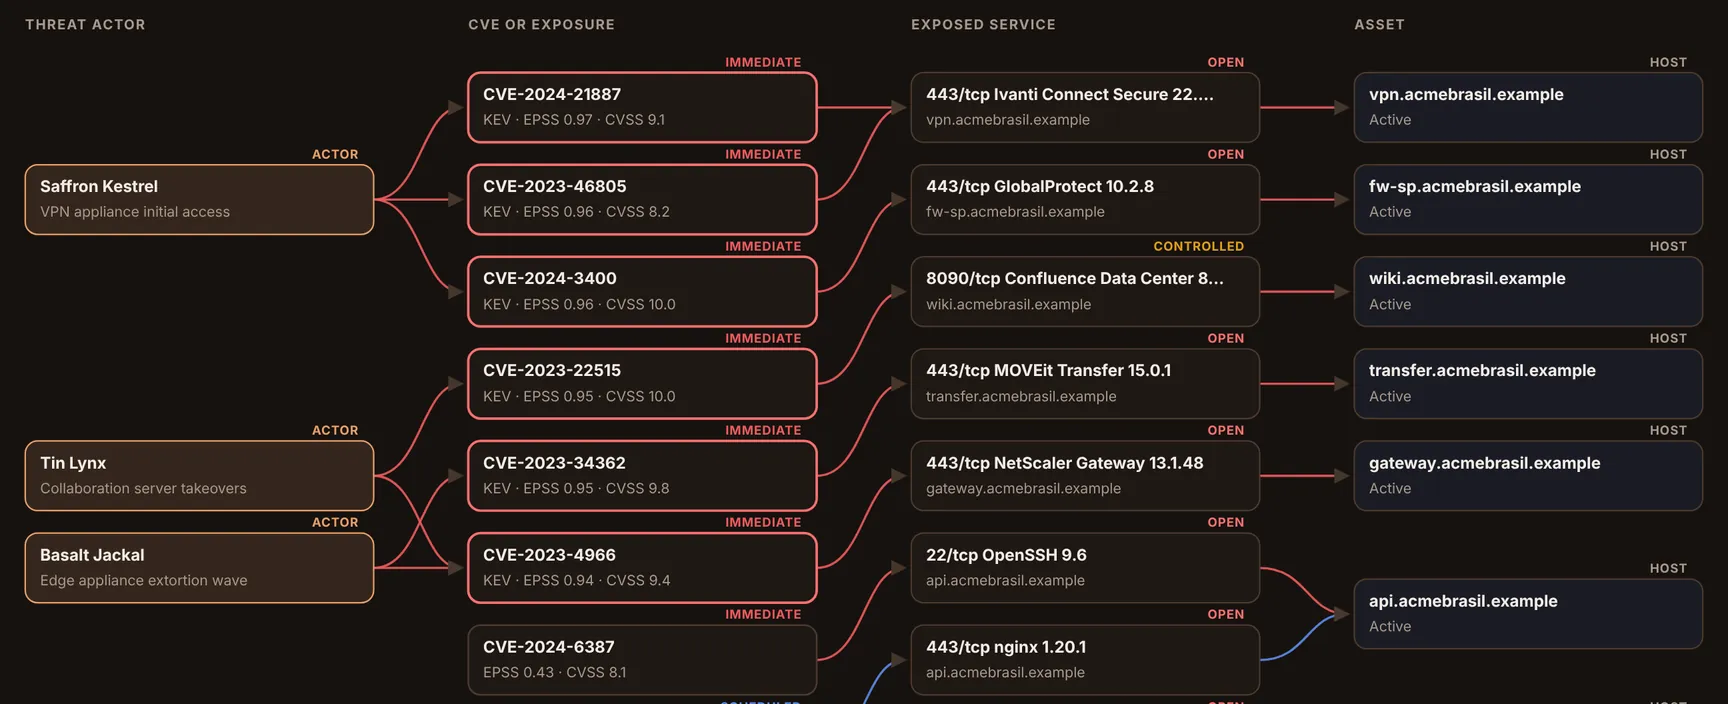
Real console screens with the demonstration tenant, with fictitious data.
See Pyris Sentra on your own environment
A 30 minute walkthrough with our specialists, using a demonstration tenant and your own use cases.
What it is
Pyris Sentra is an EASM platform fused with Cyber Threat Intelligence. It continuously discovers an organization's internet facing assets, matches every exposure against live threat context and produces a decision, not just a number, about what to fix and in what order. Prioritization follows the SSVC decision tree with EPSS ranking, so every decision is explainable and defensible.
Why it is different
A KEV listed, internet facing, actively exploited medium outranks a theoretical critical that is unreachable and has no exploit. That inversion is the product.
Outcomes
- A queue of what to fix first
- Mean time to fix per decision
- Changes flagged the same day
- Multi tenant for MSSPs
Core capabilities
- Passive discovery through certificate transparency, DNS and public sources, with attribution confidence
- Optional, in-scope active discovery: ports, services, versions and technologies
- Findings without a CVE: an exposed sensitive port, an invalid certificate and legacy TLS
- Fusion with threat intelligence: CVE, EPSS, CISA KEV, actors and campaigns
- SSVC tree with EPSS ranking, analyst overrides and a four eyes rule
- A living queue: a new KEV entry or an EPSS jump reprioritizes with no rescan
Innovation
What sets it apart
Agent and Agentless
Agentless from the outside in, with nothing to install; an Agent inside the network for the internal surface.
Change detection
A new asset, an opened service or a changed version becomes an event the same day.
Four eyes overrides
An analyst adjusts an answer; lowering a decision needs a second analyst.
Posture report
Where you stand and how long fixing takes, with no composite score.
Webhooks and OCSF
Signed events to the SIEM, SOAR or ITSM, with the whole SSVC path.
Cloud assets
Discovery in AWS, Azure and Google Cloud, with the same decision.
Proof by Pyris Hunter
Offensive validation of the exposure under the customer's authorization.
Air-gapped
An appliance inside the perimeter, with an offline intelligence bundle.
Benefits
An explainable decision
Every queue position shows the SSVC path that put it there, ready for audit.
Always current
New assets, changes and a daily re-evaluation by threat intelligence.
No noise
What is not yours, not reachable or not exploited does not rise in the queue.
Secure by design
Scope enforced in code, passive before active and one single way out.
Built for
Deployment
Operating modes
Request a demo
Want to see Pyris Sentra in action?
Tell us a little about your environment and a specialist will reach out within one business day to schedule a personalized demo.
- Live walkthrough of the Dashboard and Attack Path
- Mapping to your use cases and compliance needs
- Deployment options: SaaS, on-premises or air-gapped