Pyris Identity · Identity Security Posture
Fewer alerts. Real incidents.
ITDR for human identities, non-human identities and AI agents
Hundreds of daily anomalies become fewer than ten investigated incidents, validated by several AI models and narrated in your team's language.
Real?
It passed the deterministic gate and reached quorum in the model council.
How far?
The identity, its owner, its privilege and everything it can reach.
Now?
Recency and activity: a dormant account that woke up last night is a different story.
Actionable?
A typed response plan and a narrative read in ninety seconds.
Real console screens
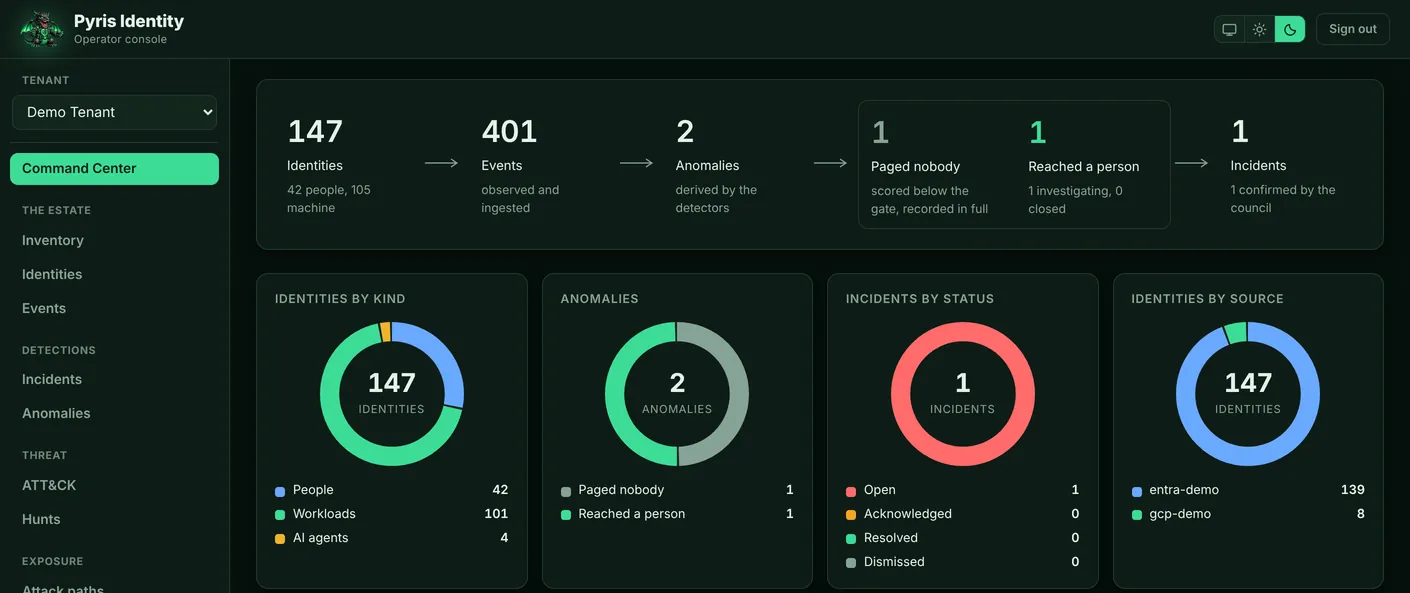
Dashboard
The whole funnel on one screen: identities, events, anomalies, what the gate held back, what reached a person and the incidents. What was silenced is shown at the same weight as what was escalated.
What sells
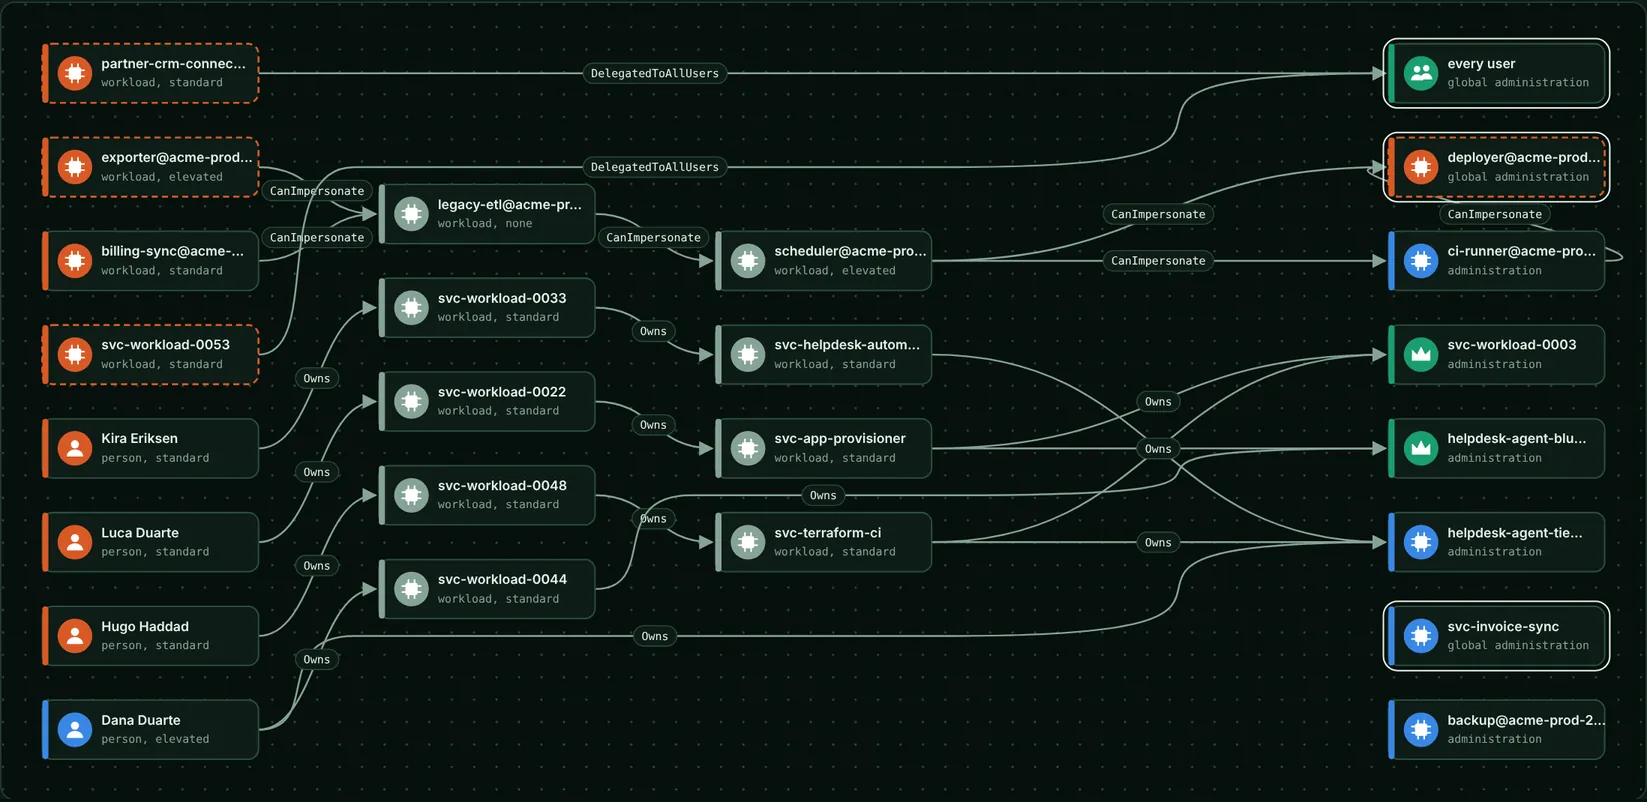
Attack Paths
From every way in (an exposed credential, an outsider, an app every user consented to, dormant privilege) to administration, by the shortest route through control edges and delegated grants.
- In the demo: 13 paths, 6 to global administration, 8 through a way in an outsider already holds
- A new path to administration is a detection on its own
Real console screens with the demonstration tenant, with fictitious data.
See Pyris Identity on your own environment
A 30 minute walkthrough with our specialists, using a demonstration tenant and your own use cases.
What it is
Pyris Identity is an ITDR platform. It continuously reads the customer's identity providers, builds a living inventory of every identity (people, service accounts and AI agents), correlates it with exposed credentials and attack paths, and runs every anomaly through a council of AI models before anything reaches a person. The output is not an alert feed: it is a few fully investigated incidents.
Why it is different
Every incident answers four questions at once. Anything that cannot answer all four is context, and it never wakes anyone up.
Outcomes
- Fewer than ten real incidents a day
- Queue ranked by impact, confidence and urgency
- An audit trail ready for compliance
- Multi tenant for SOCs and MSSPs
Core capabilities
- Entra ID, Google Workspace, Okta, PingOne, Auth0, OneLogin, JumpCloud, Active Directory, AWS and Google Cloud
- Non-human identities that are orphaned, over-privileged, dormant or holding old credentials
- Credential Truth Engine: breaches matched against real rotation, never testing a password
- Password spray, MFA fatigue, persona deviation, consent and privilege grants
- Attack Paths, blast radius and MITRE ATT&CK mapping
- Agentic AI Privilege Control, Supply Chain Identity Guard and Identity Deception
Innovation
What sets it apart
AI agents
Which identities are agents, what each can reach and when access grows.
Identity Deception
Decoys the customer declares: any touch on them becomes a signal.
Response plan
Typed steps with what each revokes, in Slack, Teams, email or webhook.
SIEM and SOAR
Incidents in OCSF and a bidirectional lifecycle with the SIEM.
Supply chain
Third parties acting inside the estate and how far each reaches.
Hunts
Saved and scheduled event log searches, with intelligence indicators.
Agent and Agentless
Agentless over API for cloud and SaaS; an Agent inside the perimeter for on-premises directories such as Active Directory.
PT, ES and EN
Narratives and plans in the tenant's language, not just a translated interface.
Benefits
Silence that works
400 failed logins from a scanner wake nobody. An orphaned account holding Global Admin does.
An auditable verdict
Every council vote is recorded, with dissent kept visible.
In the analyst's language
Native investigation narratives in Portuguese, Spanish and English.
Read only
Nothing is written to your identity provider. The platform recommends, a person decides.
Built for
Deployment
Operating modes
Request a demo
Want to see Pyris Identity in action?
Tell us a little about your environment and a specialist will reach out within one business day to schedule a personalized demo.
- Live walkthrough of the Dashboard and Attack Path
- Mapping to your use cases and compliance needs
- Deployment options: SaaS, on-premises or air-gapped